

On July 18, 2025, the Our on-line world Administration of China (“CAC”) issued an announcement (“Announcement”) launching a compulsory on-line registration system and requiring “private data processing entities” (equal to “information controller” below EU’s Common Information Safety Guidelines) that course of private data of 1 million or extra people to report the small print of their private data safety officer (“DPO”) via the “Private Info Safety Enterprise System.”
This growth follows the finalization of the Measures for Private Info Safety Compliance Audits (“Audit Measures”), efficient Might 1, 2025, which clarified the DPO tasks in conducting audits and confirmed the appointment threshold (i.e., 1 million people).
The duty to nominate a DPO has been in place since China’s Private Info Safety Regulation (“PIPL”) took impact in 2021. Underneath the PIPL, entities processing information that exceeds “a sure quantity” are required to nominate a DPO and to report sure details about the DPO — to incorporate title and speak to data — to CAC. Nevertheless, the precise threshold triggering this requirement was not outlined till the discharge of the Audit Measures in February 2025. The Announcement now gives additional element on the reporting course of.
The chart beneath outlines the important thing necessities relating to the DPO reporting.
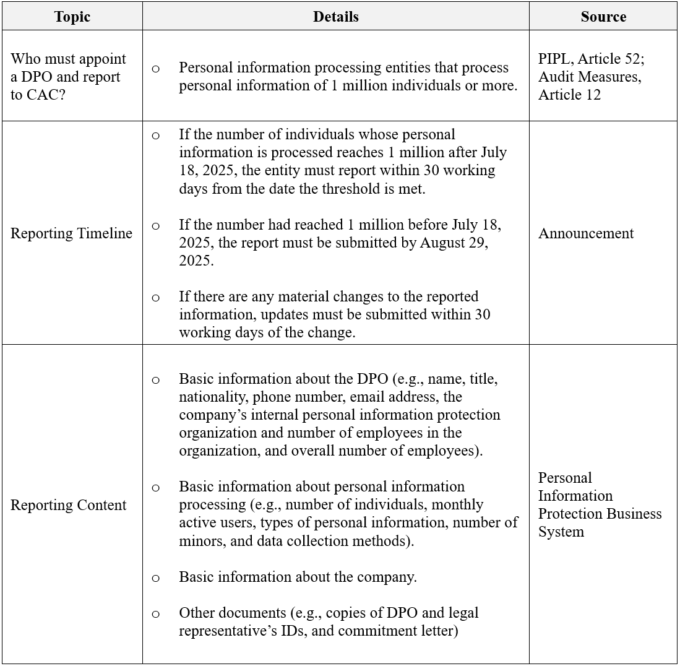
Notably, the DPO is liable for finishing up private data safety compliance audits in response to the Audit Measures. Underneath the Audit Measures, large-scale information processing entities (outlined as these processing private data of greater than 10 million people) should conduct audits a minimum of as soon as each two years. Different information processing entities are required to hold out audits “commonly,” with non-binding steering suggesting a frequency of as soon as each 5 years as an excellent follow.
As a part of the audit, the next points associated to DPO appointment ought to be assessed:
- Whether or not a system has been established to guage the efficiency of the DPO and related personnel;
- Whether or not the DPO has related work expertise and experience, and is acquainted with private data safety legal guidelines and administrative rules;
- Whether or not the DPO has clear and outlined tasks and is granted ample authority to coordinate internally;
- Whether or not the DPO has the authority to supply related opinions and solutions previous to decision-making for important issues associated to private data processing;
- Whether or not the DPO has the authority to cease non-compliant private data processing practices entity and take obligatory corrective actions; and
- Whether or not the private data processing entity publicly discloses the contact data of the DPO and submits the DPO’s particulars — together with title and speak to data — to the regulator.
Failing to nominate a DPO upon assembly the brink, or to adjust to the related reporting obligations, constitutes a violation of the PIPL. Firms processing massive volumes of private data in China ought to promptly assess whether or not they meet the 1 million particular person threshold and, in that case, take steps to finish the reporting.